

Don’t miss the AMA with Black Hat speakers Lidor B. (thisis0xczar) and Elad Meged, vulnerability researchers at Novee Security, live tomorrow, Monday, Aug 17, from 12 PM to 1 PM PT.
During the session, we will learn about:
Pre-auth remote code execution in enterprise Java platforms.
How one GitHub issue can hijack AI coding agents from Anthropic, Google, and OpenAI.
Where offensive security is heading as AI lands on both sides of the fight.

Lidor presented pre-auth remote code execution chains in enterprise Java platforms, reaching internal execution surfaces through routing logic, unsafe deserialization, and template evaluation. These platforms sit at the core of large organizations, which makes a working pre-auth chain about as high impact as a finding gets.
Elad published research showing how a single untrusted GitHub issue could compromise Claude Code, Gemini CLI, and Codex, leading to remote code execution and credential theft. As developers hand AI agents real privileges on real systems, the question of what an attacker can do with one piece of poisoned input stops being theoretical.
Read the research: Pre-Auth RCE in Enterprise Java, plus Critical Flaws in Anthropic, Google, and OpenAI’s Coding Agents.
Guest Credentials:
Lidor B. (thisis0xczar), founding-team vulnerability researcher at Novee Security and Black Hat speaker, who found pre-auth remote code execution in widely deployed enterprise Java platforms.
Elad Meged, founding-team vulnerability researcher at Novee Security and Black Hat speaker, whose work turned the AI coding agents from Anthropic, Google, and OpenAI into attack vectors through a single GitHub issue.
Ask Them Anything About
Pre-auth remote code execution and how these chains come together (Lidor)
Deserialization, routing logic, and template evaluation attacks in widely deployed enterprise platforms (Lidor)
Hijacking AI coding agents through a single GitHub issue (Elad)
Turning Claude Code, Gemini CLI, and Codex into attack vectors, and what breaks when AI agents get high-privilege access to real systems (Elad)
Using offensive AI to find real vulnerabilities
What it is like presenting at Black Hat
Where AI and offensive security are heading
Getting into vulnerability research and how they work day to day
…anything else on finding and exploiting bugs
They are live tomorrow, Monday, Aug 17, 12 PM to 1 PM PT. Leave your questions in advance and they will get to them when the session starts.
Join PWN on Reddit
PWN is where security people go to stay ahead.
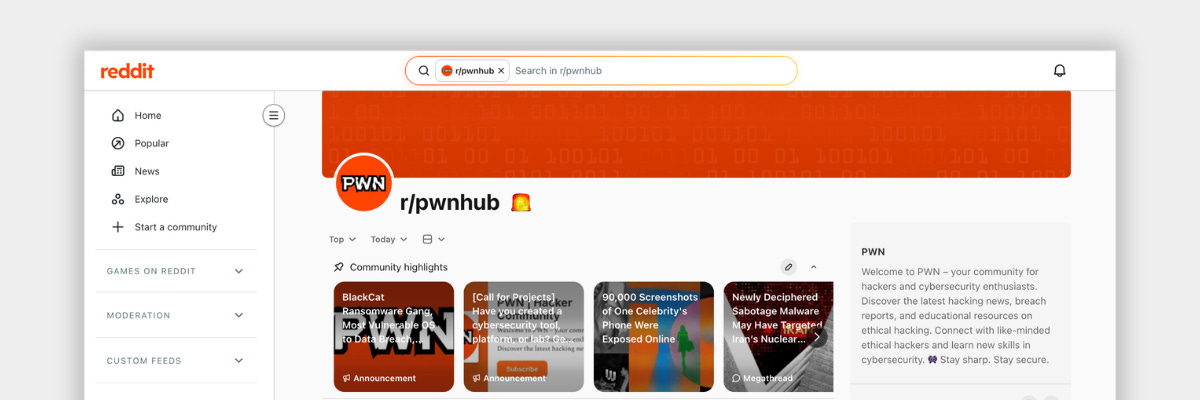
Breach reports, exploits, vendor advisories, and the kind of conversations that make you better at your job, all in one feed.
We’re 41,000+ hackers and cybersecurity enthusiasts strong, with 935,000 monthly views and 200+ new members every day.
You’ll be in the same threads as journalists from Wired Magazine, Electronic Frontier Foundation, 404 Media, Fast Company, CNET, The Guardian, Daily Mail, and Ars Technica breaking the stories firsthand, plus security teams from vendors like Proton, Intigriti, and Hudson Rock sharing research and answering questions directly.
Why join:
Know what’s hitting before it hits you. Get the breach reports, exploits, and vendor advisories early so you can act before they become your problem.
Get sharper, not just busier. Skip the noise and learn from people actually doing the work, on the AI exploits, new defenses, and techniques that move your skills forward.
Make the career move you’ve been planning. Whether it’s your first paycheck in security or your jump from IT into offensive work, you’ll find members who’ve made it and are happy to help you do the same.
Be the person at work who already knows. Walk into Monday meetings ahead of the ransomware incidents and zero-days landing on your team’s radar, and earn the trust that comes with it.
Find your people. Trade ideas with hackers and pros who’ll actually answer your questions, in a community that stays high quality because the bots and noise get cleaned up.